Cybersecurity · Guide · ~10 min
Cybersecurity in the enterprise — protecting IT infrastructure
Zero Trust, MFA, network segmentation, EDR, SIEM monitoring and ransomware-resilient backup — Alterkom’s practical approach.
Effective enterprise security combines network architecture, access control, data protection, monitoring and incident readiness — not a single firewall or antivirus product.
Modern IT spans on-prem data centres, cloud, virtualization, mobile devices and remote access. Each can become an attack surface.
Key challenges
- Phishing and account takeover.
- Ransomware and malware.
- Unpatched vulnerabilities and misconfiguration.
- Privileged account abuse and supply-chain risk.
Many incidents chain several weaknesses rather than exploiting one flaw.
Zero Trust — no implicit trust
Verify every access request using identity, permissions, device posture and context. Combine MFA, least privilege, segmentation, app-level access and continuous monitoring.
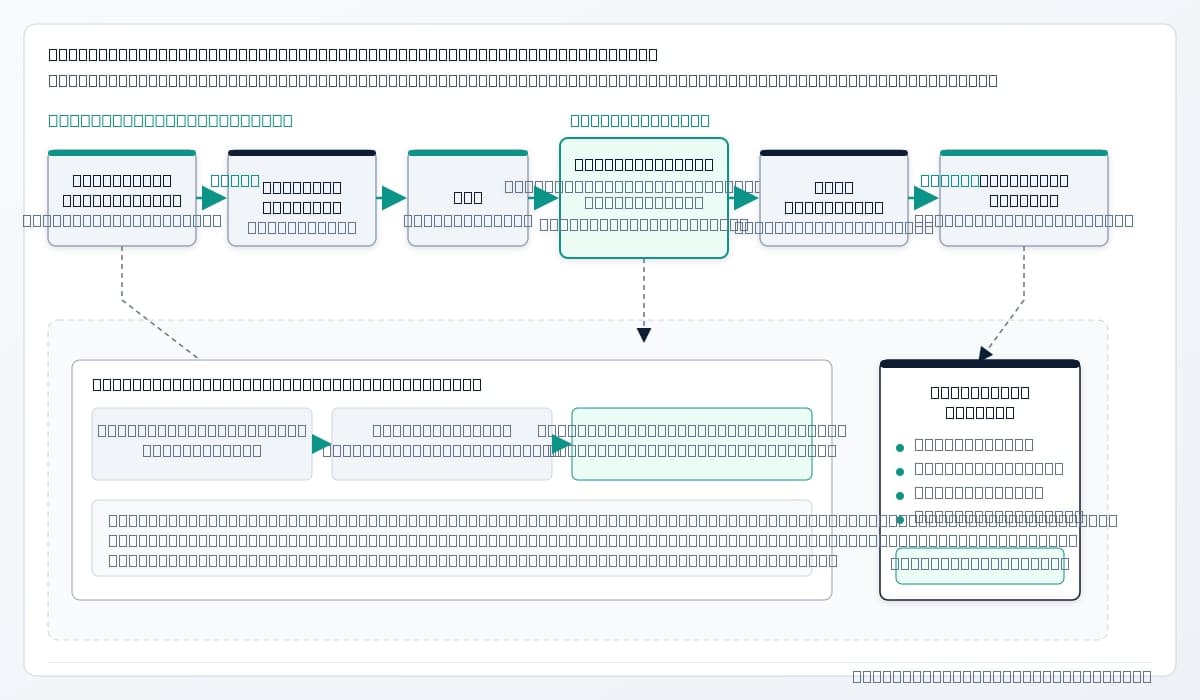
Zero Trust architecture
Identity, MFA, policy engine, device posture and application access — with audit and monitoring. A model, not a single product.
MFA and network segmentation
Protect admins, VPN, mail, cloud consoles and sensitive apps with phishing-resistant MFA where possible. Segment admin, production, users, guest Wi‑Fi, backup and DMZ zones.
Endpoints, servers and backup
Patching, hardening, EDR and inventory reduce risk. Ransomware-resilient backup needs separation, immutable repositories, isolated copies and tested restores — not just successful job logs.
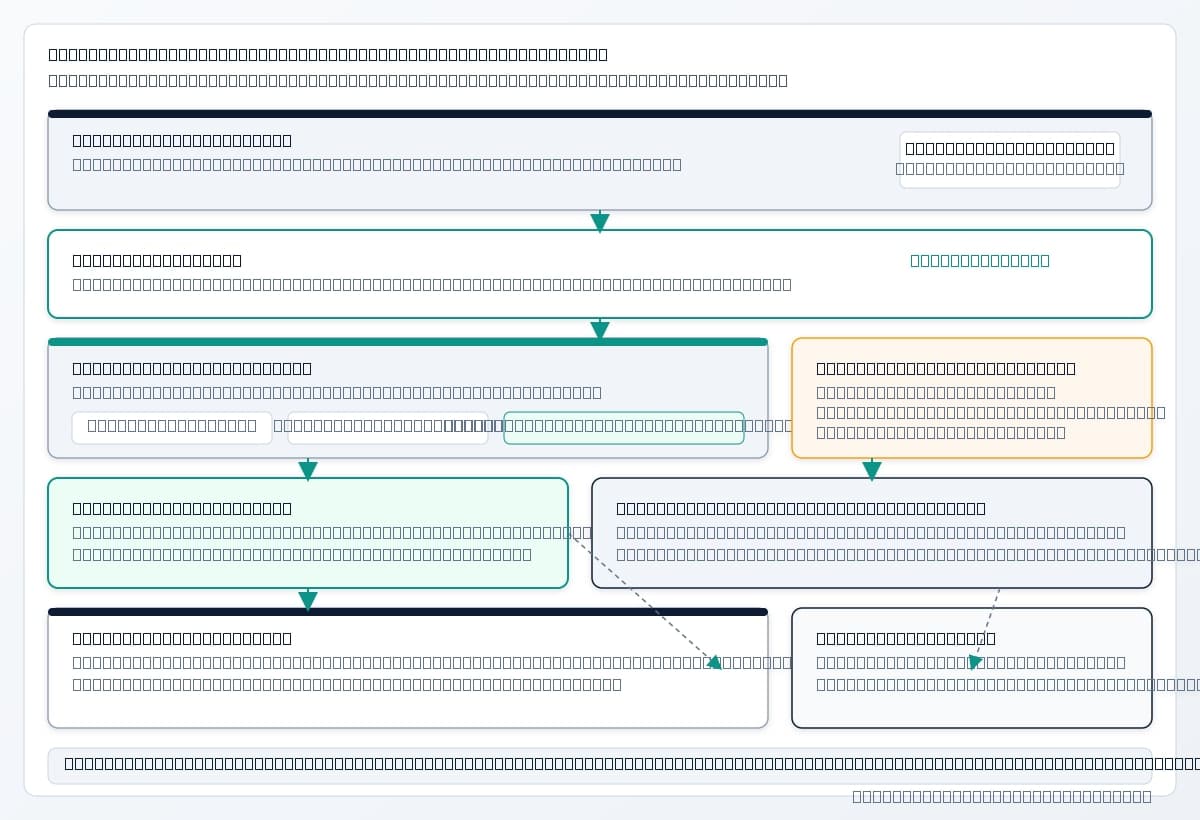
Ransomware resilience
Segmentation, dedicated backup infrastructure, immutable storage, air-gapped copies and recovery drills — with split admin privileges.
Monitoring, virtualization and incidents
SIEM/EDR visibility, hypervisor and cluster admin protection, and a documented incident response plan with regular exercises. Start with MFA, patching, segmentation, backup hardening and monitoring.
Alterkom designs and delivers layered security for IT infrastructure, access, networks and data.
FAQ
Is a firewall enough?
No — you also need identity controls, patching, segmentation, endpoint protection and monitoring.
Does MFA stop all account takeover?
It greatly reduces risk; method choice and recovery-process security matter.
Does backup prevent ransomware?
It enables recovery but does not stop the attack itself.
EDR vs SIEM?
EDR focuses on endpoints; SIEM correlates events across the environment.
Zero Trust on existing infrastructure?
Yes — typically phased: identity, permissions, segmentation and app access.
Related catalog products
Storage and servers supporting data protection strategies.
Related focus areas
Topics linked to layered IT security.
Cyberbezpieczeństwo
Tożsamość, sieć, endpointy, monitoring i reagowanie na incydenty.
Zobacz obszar
Infrastruktura IT
Serwery, hardening i środowiska produkcyjne.
Zobacz obszar
Storage
Backup, immutable copies i ochrona danych.
Zobacz obszar
Wirtualizacja
Bezpieczeństwo hostów, klastrów i sieci migracji.
Zobacz obszarRead also
Other materials from Knowledge.
Lokalne AI w firmie – jak wdrożyć własną sztuczną inteligencję?
Private AI, lokalne modele LLM, infrastruktura GPU i RAG z kontrolą nad danymi firmowymi.
Czytaj więcej
Wysoka dostępność serwerów – jak zapewnić ciągłość działania infrastruktury IT?
Klastry HA, redundancja serwerów, sieci i storage, RPO/RTO oraz Disaster Recovery.
Czytaj więcejStrengthen your infrastructure against cyber threats
We help assess security architecture, deploy access controls, harden infrastructure and design data protection strategies.
Recommended by Alterkom
Solutions, focus areas and products related to this article — a path into our offer.